Protect your business.Know where you stand.
Your business depends on the information, accounts and systems your team uses every day. We help you identify security gaps, prioritise improvements and put practical protection in place.
MIT Sunshine Coast helps Australian businesses strengthen their cybersecurity posture through practical security solutions aligned with the Australian Cyber Security Centre’s Essential Eight framework and recognised industry best practices.
Local expertise. Clear priorities. Practical improvements.
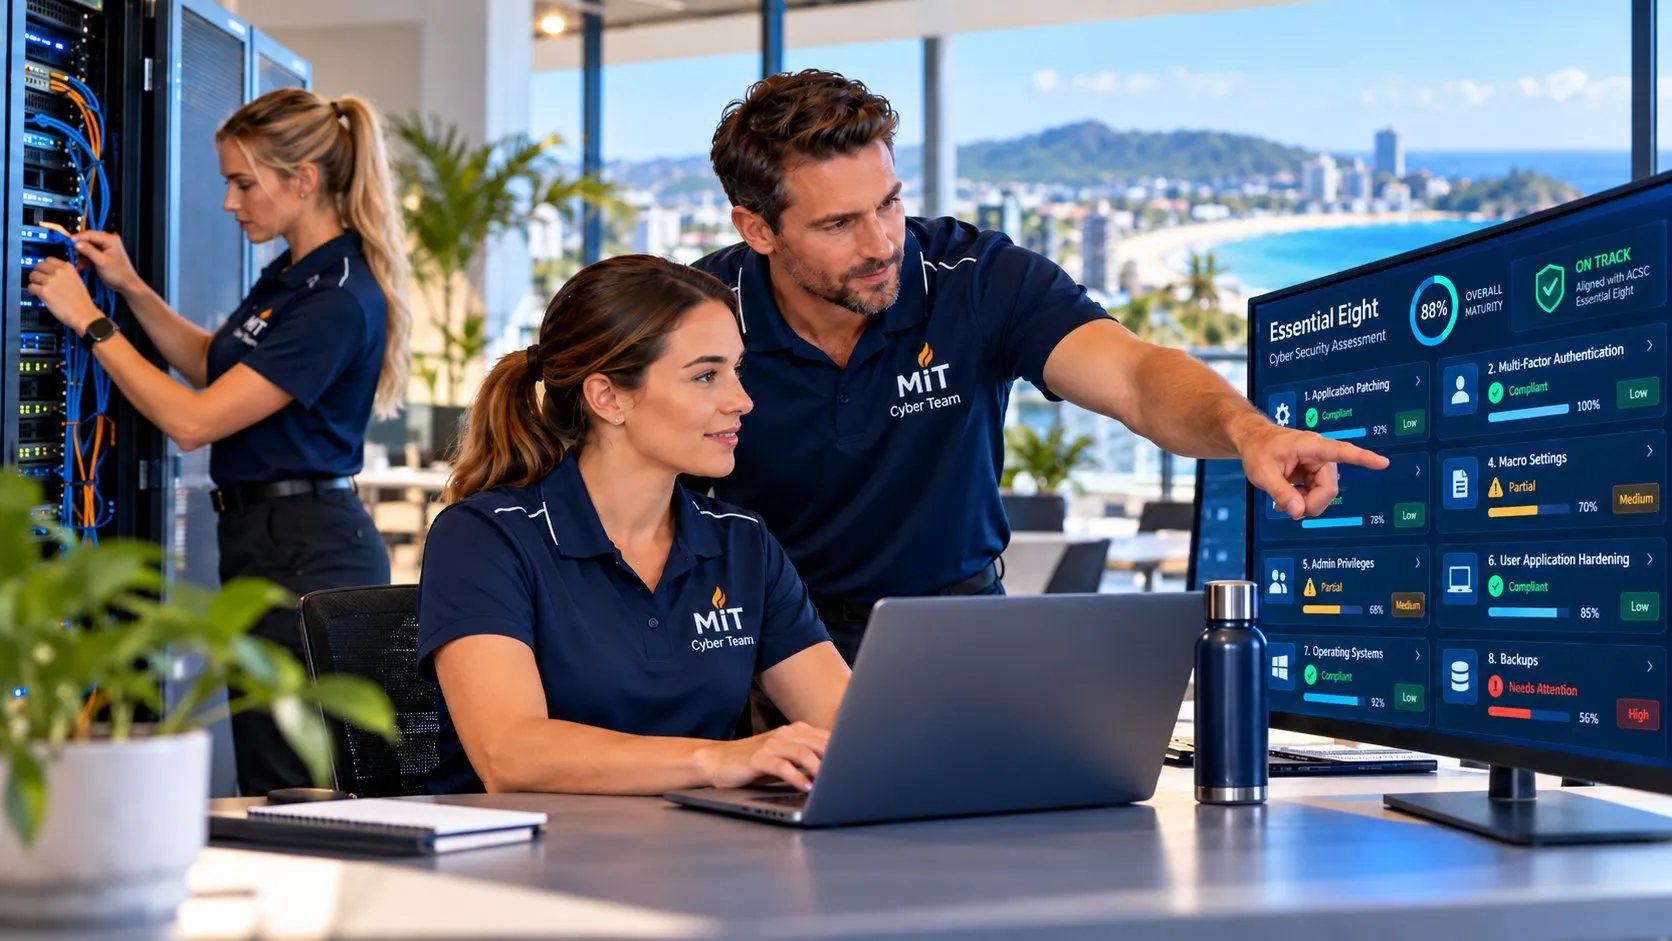
Confidence starts with knowing what needs attention.
Are your business accounts properly protected? Can former staff still access information? Would your backups help you recover? Are important security updates being missed?
We help Sunshine Coast businesses replace uncertainty with clear findings and practical next steps, so you can make informed decisions about protecting your business.
Protect important information
Reduce exposure across business accounts, devices and shared data.
Reduce avoidable disruption
Address weaknesses that could interrupt your operations.
Spend where it matters
Prioritise improvements around risk and business impact.
Prepare for an incident
Clarify recovery arrangements and who needs to act.
A clear target, supported by evidence
Essential Eight maturity levels run from Zero to Three. We help define a suitable target and document findings against the applicable requirements within the agreed scope.
The Essential Eight is a baseline, not a complete cybersecurity programme. Additional controls may be needed for your systems and risks. Read ASD’s Essential Eight guidance
Eight strategies, assessed against the target you choose.
The Australian Signals Directorate’s Essential Eight sets out eight mitigation strategies. We review how each one is implemented in your environment and where the gaps are.
We look at your business the way an attacker would.
Security tools and checklists matter, but attackers don’t follow checklists. Members of our team attend DEF CON and BSides, and have attended Black Hat, where security researchers show how real attacks work.
We bring that back to Sunshine Coast businesses in plain English: what attackers are doing now, what they could find in your business, and what to fix first.
- Start with what an attacker can see and reach
- Fix the gaps most likely to be used, first
- Test that controls work, not just that they exist
- Explain the risk in business terms, not jargon
Findings you can act on.
Every cybersecurity assessment includes a documented scope, business-focused executive summary, security control findings, prioritised remediation recommendations and a review discussion to help you understand your risks and make informed security decisions.
- Executive summary
- Main findings explained in plain English.
- Defined scope
- Systems reviewed, limitations and exclusions.
- Control findings
- Evidence of what is implemented and where gaps remain.
- Prioritised remediation
- Recommended improvements, dependencies and responsibilities.
- Findings review
- An opportunity to work through findings and next steps.
A cybersecurity assessment is not automatically equivalent to a penetration test, formal compliance audit or independent certification.
Assessment activities, testing methods, reporting detail and deliverables are confirmed as part of the agreed engagement scope.
For healthcare and other compliance-sensitive organisations, we also offer optional assessment mapping against relevant standards and frameworks, such as the ACSC Essential Eight, ASD ISM and ISO/IEC 27001, without implying formal certification or accreditation.
For Essential Eight work, we confirm up front whether the engagement is a preliminary gap review or a formal maturity assessment. A questionnaire alone doesn’t establish a verified maturity level.
Start with the areas that matter to your business.
Essential Eight assessment
Review the agreed environment against applicable Essential Eight requirements and identify gaps against your chosen target.
Microsoft 365 security review
Review identity and access settings, administrator permissions, email configuration and sharing controls. Examine available sign-in and audit information within the agreed scope.
External exposure review
Review agreed internet-facing assets and configurations to identify exposed services, outdated systems and weaknesses requiring attention.
Phishing awareness and simulations
Help staff recognise and report suspicious messages, with authorised simulations and practical follow-up where included.
Network and onsite security review
Review areas such as Wi-Fi separation, network access, device configuration and physical access to communications equipment.
Incident readiness exercise
Work through a realistic scenario to clarify responsibilities, escalation, communications and recovery priorities.
Each review has an agreed scope and deliverables. Vulnerability reviews and Essential Eight assessments are distinct from penetration testing.
Put your security improvements into practice.
Once the priorities are clear, we can help implement and manage the agreed controls across your environment.
Your proposal identifies the technologies, licensing, management responsibilities and support arrangements required.
- Device and endpoint protection, including OpenText antivirus
- Account security, MFA and administrative access
- Application and operating system patching
- Application control and hardening
- Email protection and staff awareness
- Backup protection and recovery testing
Advanced Antivirus & Endpoint Protection
OpenText Core Endpoint Protection
Powerful protection for the devices your business depends on.
Every business computer, laptop and server can become a target for cybercriminals. Protecting these devices is an important part of reducing cybersecurity risks and preventing avoidable business disruption.
MIT Sunshine Coast supplies OpenText™ Core Endpoint Protection, formerly known as Webroot Business Endpoint Protection, through convenient annual subscriptions.
OpenText combines cloud-based threat intelligence, behavioural analysis and automated threat prevention to help safeguard your business against malware, ransomware, phishing-related threats and emerging cyberattacks.
What does OpenText protect against?
Viruses and malware — Helps detect, block and remove malicious software, including viruses, spyware, Trojans and other harmful programs.
Ransomware attacks — Detects suspicious activity associated with ransomware, helping prevent infections and supporting automated remediation.
Phishing and malicious websites — Helps identify and block dangerous web content, fraudulent links and malicious URLs encountered on protected devices.
Zero-day and emerging threats — Uses real-time threat intelligence and behavioural analysis to identify potentially harmful activity, including previously unknown malware.
Malicious scripts and fileless attacks — Helps detect and prevent attacks that exploit legitimate system tools and scripting technologies.
Cryptomining threats — Helps prevent malicious software from hijacking your computer's resources for unauthorised cryptocurrency mining.
Intelligent protection. Minimal interruption.
OpenText is designed to provide effective security without unnecessarily slowing down everyday work.
Key benefits include:
- Real-time protection against a broad range of cyber threats.
- Lightweight security software with minimal system impact.
- Continuously updated cloud-based threat intelligence.
- Automated threat detection, quarantine and remediation.
- Centralised management of protected business devices.
- Protection for office-based and remote workers on supported devices.
Annual antivirus subscriptions from MIT Sunshine Coast
MIT Sunshine Coast supplies OpenText endpoint protection through annual licensing, helping businesses maintain an active and up-to-date antivirus solution.
We can assist with deployment, security configuration, licence renewals and ongoing endpoint management, with support arrangements tailored to your requirements.
Whether you need protection for one business computer or an entire organisation, our team can recommend suitable licensing and deployment options.
Protect your devices. Reduce your exposure. Keep your business moving.
Enquire About OpenText Antivirus Protection
Or call 1300 68 55 46 to discuss your requirements.
OpenText endpoint protection is one component of a broader cybersecurity strategy. It does not replace secure backups, software updates, multi-factor authentication or other recommended security controls. Licensing, supported devices and management services are confirmed as part of your quotation.
Is it time to review your security?
- You are unsure how well your current protection is configured.
- Your business handles sensitive client, patient, employee or financial information.
- A customer, insurer or tender process has asked for security evidence.
- Your Microsoft 365 environment has grown without a structured review.
- Staff changes have left uncertainty about accounts and access.
- You want to understand how you would respond and recover after an incident.
You do not need to know which assessment to request. Tell us about your business and concerns, and we will help define a sensible starting point.
Discuss a security assessment

Know what needs attention. Make your next move with confidence.
Whether you need a clearer picture of your security, help with the Essential Eight or practical improvements to your existing controls, start with a conversation with our local team.
We will help define the right scope and explain the next steps.
Opens an email with a few questions to fill in.
Or call 1300 68 55 46Existing client? Log a support job